I never got into crypto, but when I was considering doing so I was pretty quickly convinced that I should use a hardware wallet to store my private keys, as these are usually considered to pose less of a risk of being hacked and stolen than storing everything online. But alas, it seems one of the most reputable hardware wallets on the market has fallen victim of a supply chain attack (via a reseller) that’s reportedly left some users short of a tidy collective sum of at least $86 million and, according to YFarmX’s calculations, potentially over $100 million.
Ledger, the hardware wallet maker in question, has since said that as part of its investigation into the reports of stolen crypto, it can indeed confirm that “one of the impacted users’ devices contained an unauthorised hardware implant.”
The company also says, “To date, all confirmed cases related to the disclosed draining incident of Oct 9th, 2026, involve devices sold through the Southeast Asia reseller CryptoBilis.”
Ledger says CryptoBillis confirms it has ceased all sales of the wallet until the ongoing investigation is concluded. The company also says it is “working with the appropriate authorities to bring the bad actors to justice.”
Judging from a disassembly of an affected device shared on Reddit, it looks like the battery was taken out to fit in the “unauthorised hardware implant.” This implant, at least according to some reports, sat behind the screen where its padding should be. Importantly, the implant seems to be soldered and takes information from the screen, thereby avoiding the usual hardware tampering detection in the device.
72 hour update on reseller CryptoBilis incident 🔽As the investigation continues, we are working with relevant authorities. The volume of impacted devices is limited. We know this is concerning, especially for those directly affected, and we are reaching out to impacted users.To date, all confirmed cases related to the disclosed draining incident of Oct 9th, 2026, involve devices sold through the Southeast Asia reseller CryptoBilis. Our systems and direct sales channels remain unaffected. We take the CryptoBilis situation seriously and are actively investigating.We encourage impacted users to reach out to Ledger Support through official channels and file complaints with their local law enforcement authorities. As a reminder, CryptoBilis has confirmed having ceased all sales of hardware wallets.We are reminding our authorized resellers and distributors to source products only through authorized channels and never to restock returned products.Also, we strongly advise users not to purchase from unauthorized resellers, where the risk of buying suspicious, counterfeit or modified devices is important as nothing operates under ledger security guidelines.Security isn’t static and this incident underscores why we continuously review and strengthen our distribution and anti-tamper processes. We are continuously improving that work now and events like this strengthen our resolution: reviewing authorized reseller controls, advancing hardware protections, and cooperating with authorities. Thanks to @SEAL_911 for their collaborative support and all their efforts.This is an ongoing threat that doesn’t just impact Ledger, but the whole ecosystem, and we are calling others in the space to work with us on making improvements for users.We believe in jointly working with researchers, other vendors and partners on improving industry chain-of-custody practices and anti-tamper techniques. Raising the bar on physical supply-chain integrity benefits the entire ecosystem. If you have relevant information, contact security@ledger.com.For CryptoBilis buyers: do not initialize unused devices. If already set up, move to a new seed on a device from Ledger. If you have concerns that your device was impacted by the CryptoBilis incident, please contact Ledger Support through the official site: https://t.co/JUcWwJO9iF. Ledger Support is available 24/7 to answer your questions and concerns.Scammers often try to take advantage of incidents like this. Rely only on official Ledger channels. Ledger will never call you, DM you, or ask for your 24-word recovery phrase.October 11, 2026
The company does show disassembly images for its hardware wallets so you can take it apart and check everything looks how it should. But these implants are apparently easy to miss unless you’re careful even with disassembly, and Ledger notes that its integrity checks “cannot detect unauthorized physical modifications to the hardware—such as spying implants—if the original Secure Element remains intact.”
So, what is the safe way to look after your crypto? It seems the community isn’t entirely certain itself, apart from keeping your keys entirely apart from tech, such as on ‘paper’ (preferably something more sturdier and durable, though).
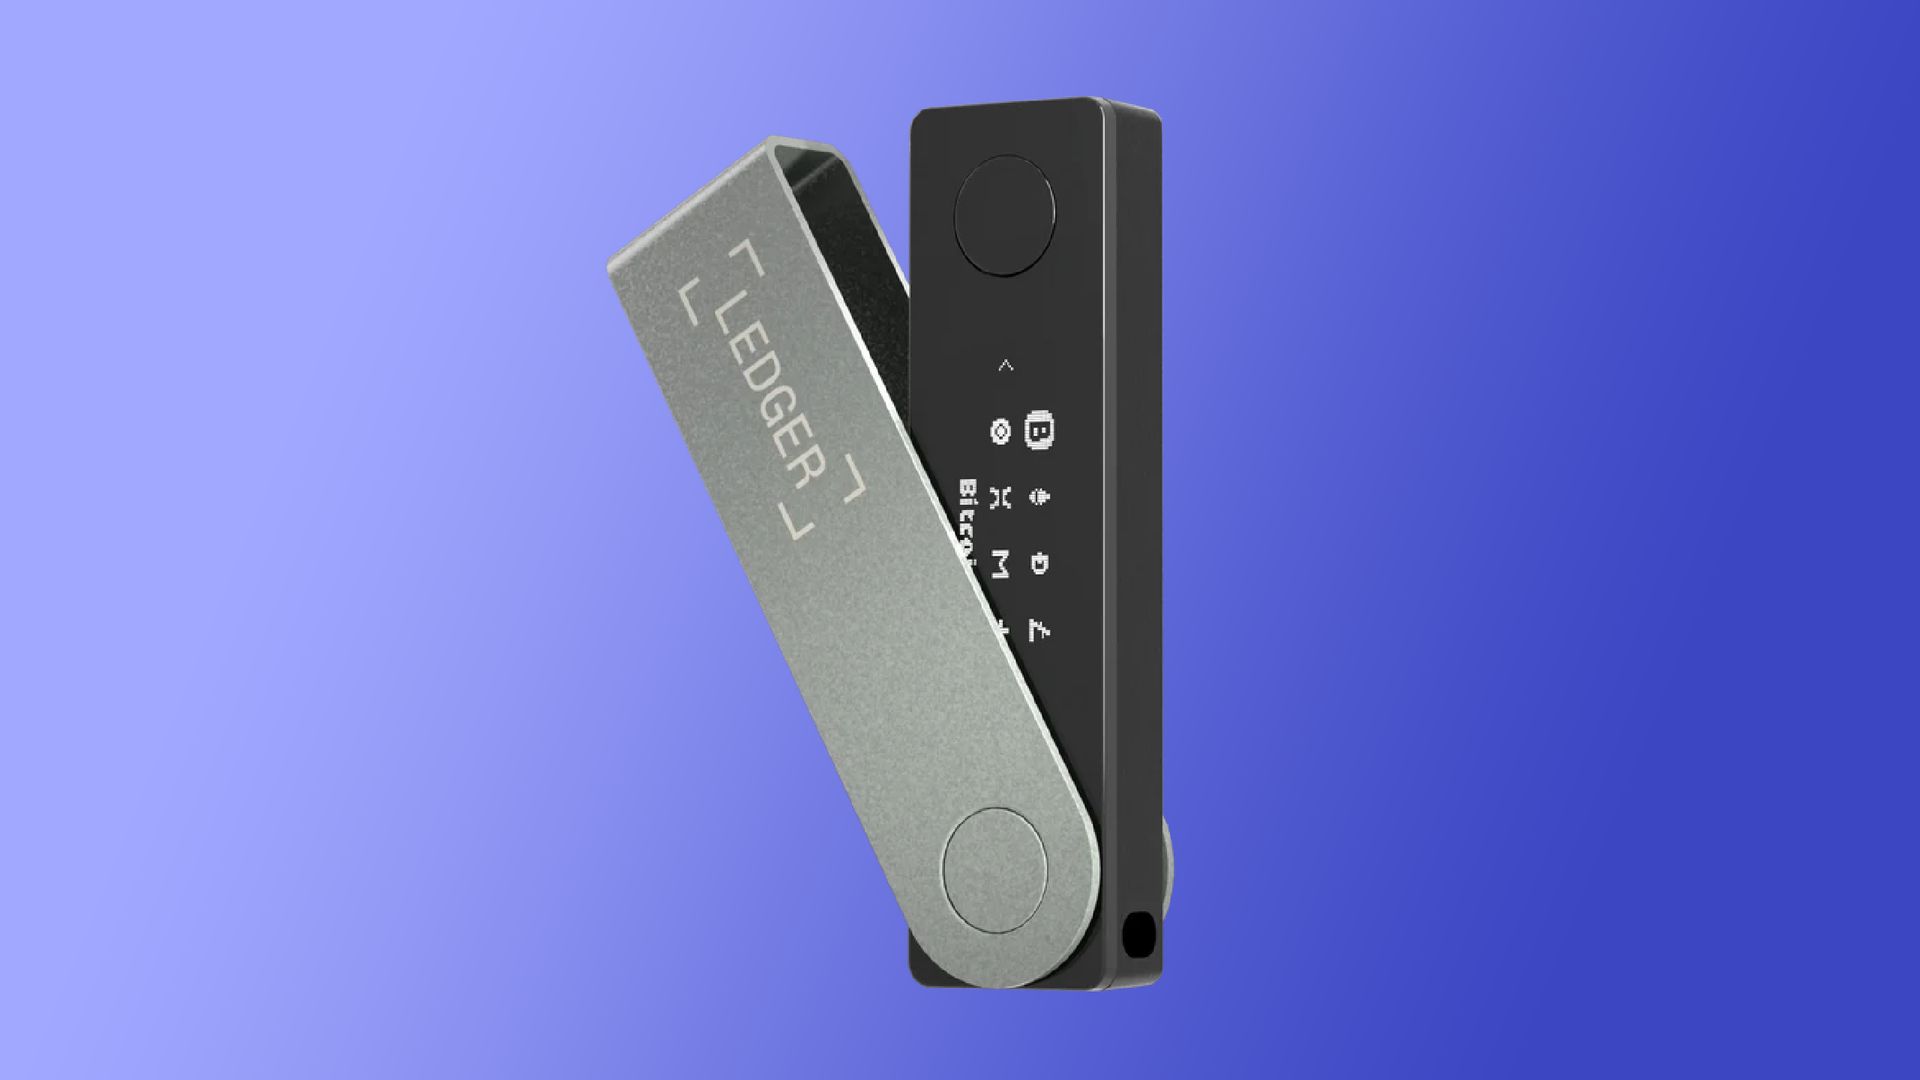
In this particular case, I would assume buying directly from Ledger might have mitigated the risk, too, though CryptoBillis was an official reseller. Anything to reduce that attack vector is a good idea, given increasing supply chain risks.
The Open Web Application Security Project (OWASP) said earlier this year that “software supply chain failures” are a big risk for web app security, and we’ve seen supply chains being targeted in other industries such as for home routers. It seems ordering from as close to the source as you can get to is extra-advisable, these days. I’d say that goes doubly so when you’re dealing with storage for vast amounts of money, crypto or otherwise.